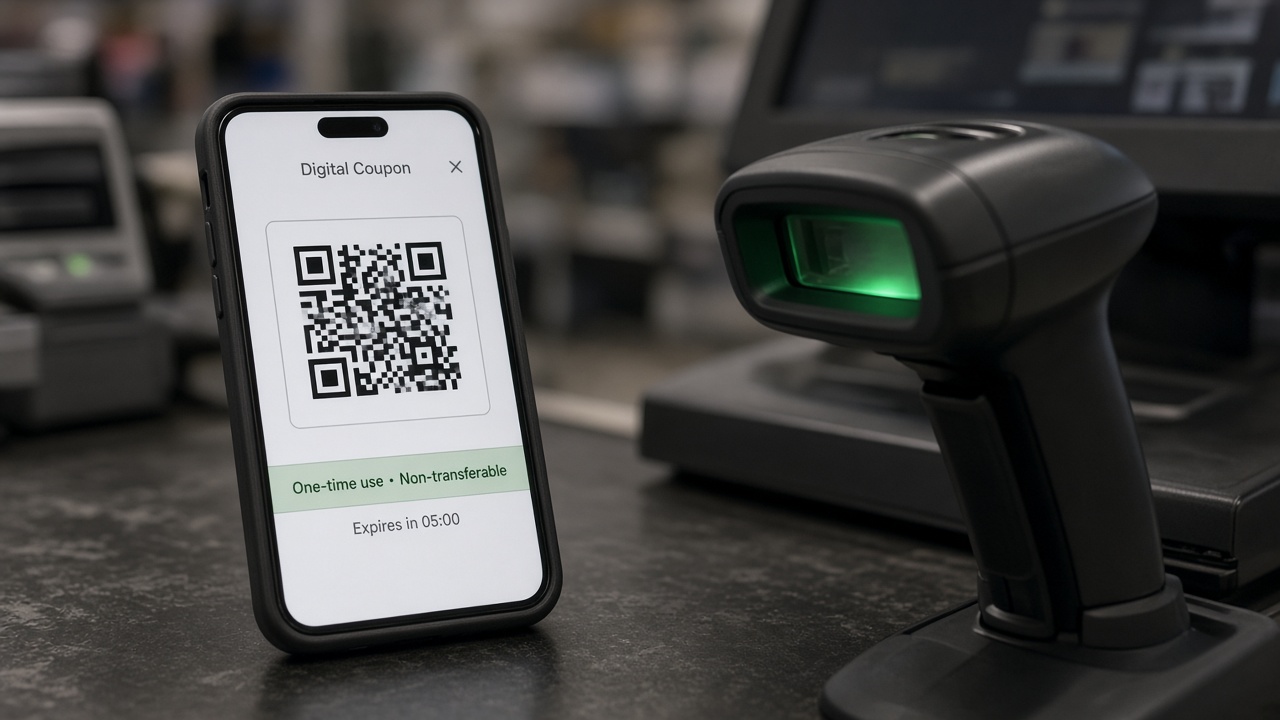
Fraud controls fail when they are bolted on after launch. Direct-marketing enforcement cases also show that promotional journeys collecting personal data for ‘simple’ incentives attract regulator attention when collection is excessive or consent is weak — coupon programmes that harvest data need the same discipline as CRM.
Pick controls that protect budget while keeping legitimate shoppers moving.
Why fraud and compliance collide on coupons
Digital codes travel. Paper coupons get photocopied. Customer data attached to redemption can become a second risk if you over-collect. Balance fraud filters with purpose limitation.
What good fraud prevention looks like
- Velocity limits per code, household, device or retailer ID.
- Geofencing or channel locks where the offer is market-specific.
- One-time codes for high-value offers; batch codes only with tight retailer controls.
- Watchlists for repeated decline patterns reviewed by a human.
- Minimal personal data at redemption — collect only what settlement needs.
Questions before you go live
- What false-positive rate will customer care accept in week one?
- How fast can marketing pause a leaking code family?
- Are retailer staff trained on acceptance rules, or only the till prompt?
How Dcode fits
Dcode runs coupon fraud management alongside clearing and digital coupon operations, so marketing mechanics and operational controls are designed together.
Next step: send offer value, channel list and expected volume via contact for a fraud-control pass.